
Open Banking Compliance
Evidence first. Every consent and every action on record.
Consent management, Open Banking directory registration steps, certificates and an append-only audit log are organised so compliance teams can see what happened, when, and who did it.
What it does
Capabilities
Each item says whether it is shown in the prototype console today or is planned. Planned items are not available.
Consent register and broker
Shown in prototypeView consents by bank and purpose, and route requests through a consent broker.
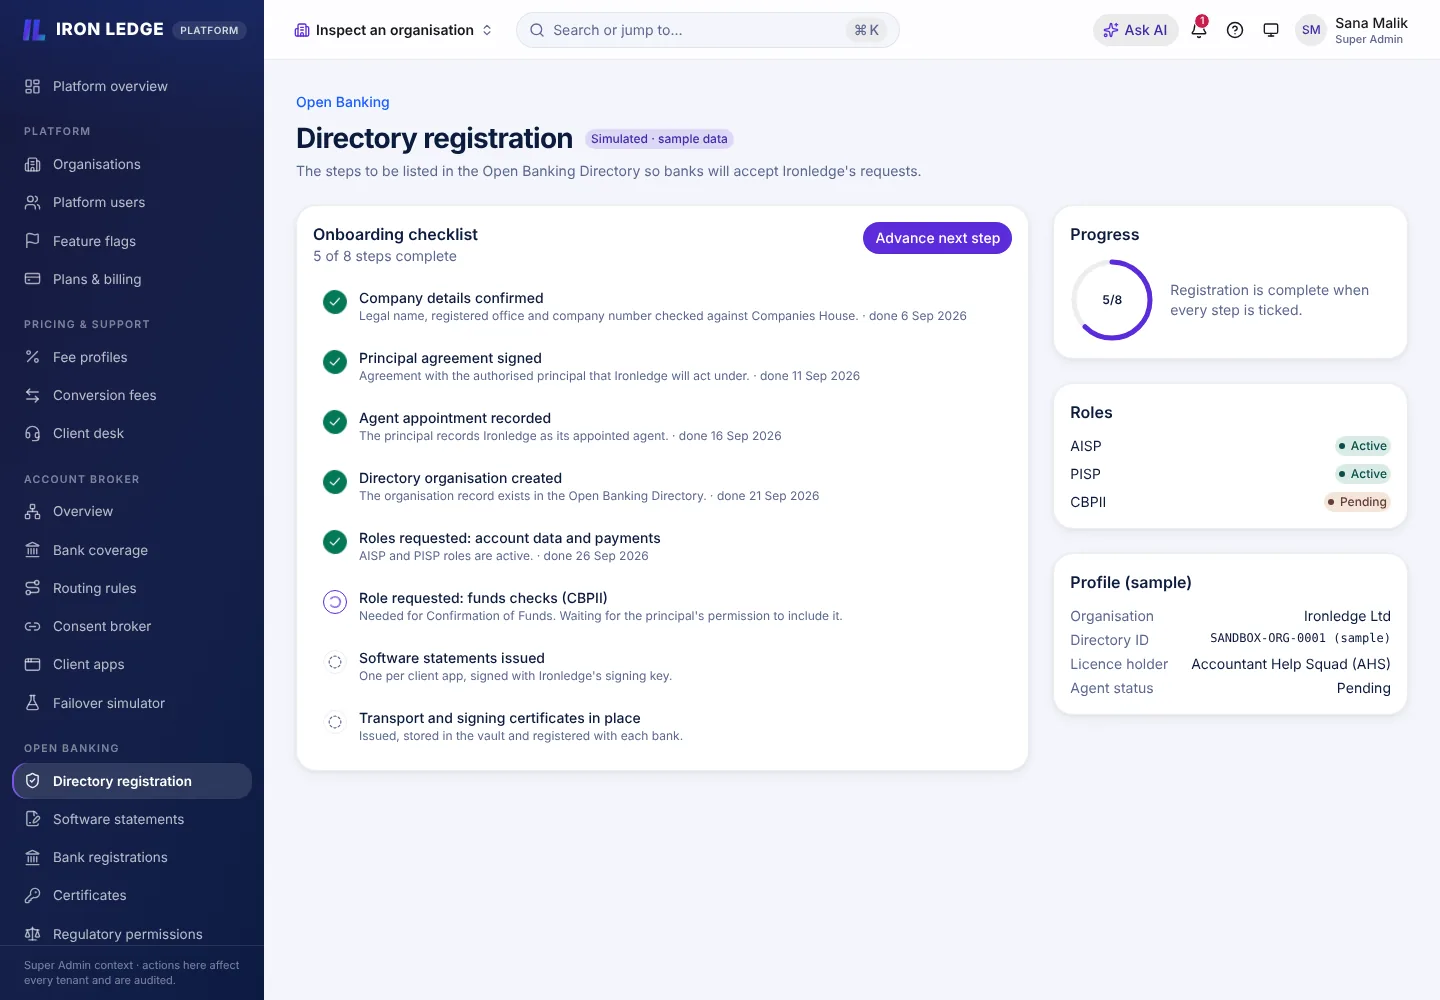
Directory registration steps
Shown in prototypeA checklist for onboarding steps, software statements and certificates.
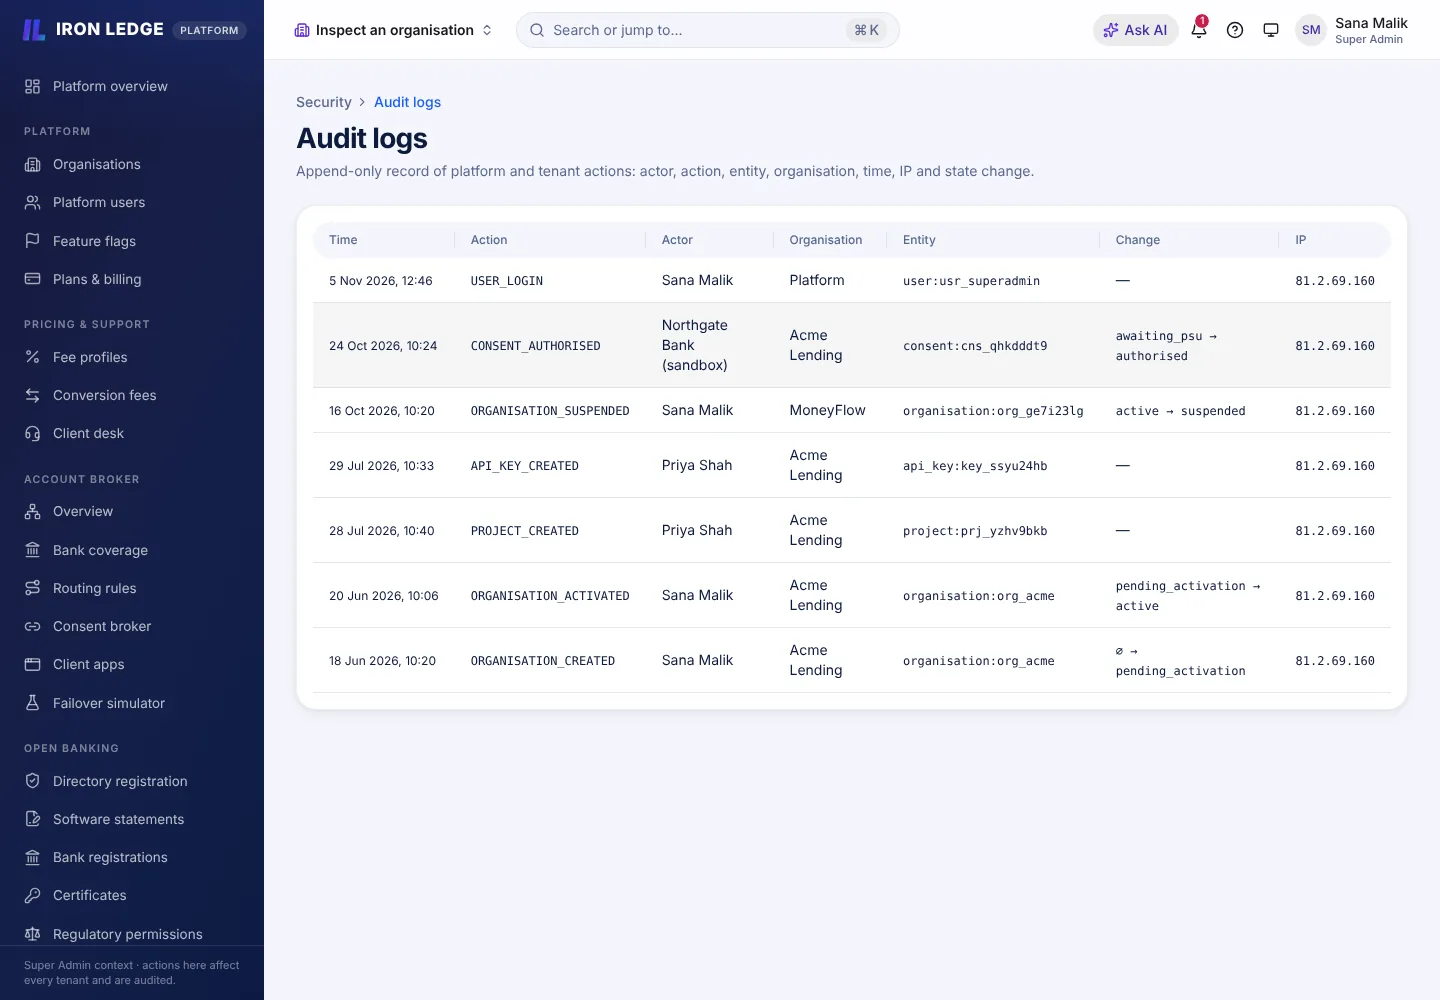
Audit log
Shown in prototypeWho did what, to which record and when, with before and after values.
Role-based permissions
Shown in prototypeRoles and permissions limit who can see or change sensitive screens.
Regulatory reporting
PlannedPackaged regulatory reports.
How it works
Four steps
- 01
Register
Work through the directory registration checklist.
- 02
Capture consent
Record purpose, permissions and expiry.
- 03
Operate
Monitor connections, certificates and bank health.
- 04
Evidence
Export audit trails for review.
In the console
Real screens from the prototype
Captured from the running prototype with simulated data.

For developers
Request shape
An illustration of the kind of data involved. API reference and SDKs are not yet published, so no endpoints are listed.
Illustrative audit entry
{
  "actor": "role:org-owner",
  "action": "consent.revoked",
  "entity": "consent_demo_01",
  "at": "2026-11-05T10:12:00Z",
  "note": "Illustrative only"
}
UK context
Regulatory background
Open Banking in the UK sits within a regime involving the FCA, Open Banking Limited, the Payment Systems Regulator and the ICO for personal data. No authorisation or certification is claimed on this website.
General background, not legal advice. No authorisation or certification is claimed on this page.
Related